Forensic Imaging & Triage
NBFTools NETRE
Triage and acquisition for Mac, Windows and Linux, including Apple Silicon and T2 decrypted images.
- Windows
- Linux
- macOS
NBFTools supports imaging, processing and analysis of data from Microsoft Windows, Apple Mac and Linux operating systems, including servers. Other file systems are supported too.
Unlock the power of mobile device forensics with NBFTools. Analyse data from iPhones, iPads and Android devices, and integrate mobile backups from other forensic tools.
NBFTools is the most intuitive digital forensic software for analysing data from cloud services, including email, chats, web history, photos and more.
15+
Years of
Experience
About Company
NBFTools Private Limited is a leading digital forensics research and development company based in India. It builds state-of-the-art forensic tools with cutting-edge technology to meet the industry's evolving needs. Experienced digital forensics experts lead the team, and with more than 15 years of hands-on experience they excel in Linux, Windows, Macintosh, Android, iOS and cloud forensics.
As an authorized NBFTools reseller, Noah Forensics Solutions brings these innovative solutions to your digital forensic requirements.
Read More (opens nbftools.com in a new tab)Why Choose Us
NBF is built on the rock-solid foundation of the Linux platform, with fully customisable features. User privacy comes first: the tools collect no user data.
We help corporations with internal investigations and support digital forensic service providers on complex cases.
We are always ready to listen to anyone who needs help with complex investigation techniques, legal strategy or the cyber world.
With a comprehensive range of forensic tools and the expertise to use them, we help government agencies solve criminal cases.
We partner with universities and colleges on industry-aligned digital forensics courses. NBFTools are available to academia at a minimal price.
Our Products
Noah Forensics Solutions is an authorized reseller of NBFTools. We supply licenses and hardware, and we support you through deployment, training and casework.
Forensic Imaging & Triage
Triage and acquisition for Mac, Windows and Linux, including Apple Silicon and T2 decrypted images.
Multi-OS Forensic Analysis
Analyse forensic images from macOS, Windows, Linux, mobile backups and the cloud, running natively on all three OSes.
iOS Acquisition & Analysis
iOS triage, acquisition and detailed analysis with a fast core engine and minimal hardware requirements.
Forensic Workstations
A purpose-built processing engine by BitMindz with an i9-13900KF, 128GB DDR5 and a built-in write-protect bay.
Flexible Licensing
Monthly TRIOS and NETRE licenses for Mac, valid for 30 days from activation.
Forensic Imaging & Triage
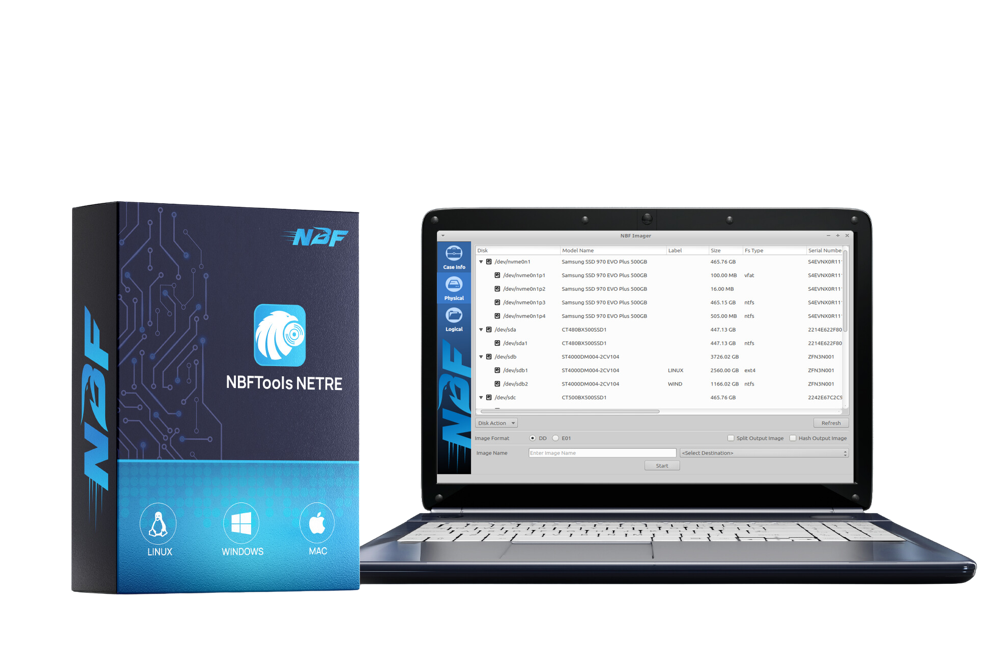
NETRE is a digital forensics triage and acquisition tool for Mac, Windows and Linux. It images to E01, DD and virtual hard disk formats in live and custom-booted environments on Intel, AMD and Apple Silicon machines. It also supports targeted collection by user profile, application or custom filter.
Monthly Mac license available. Request a license
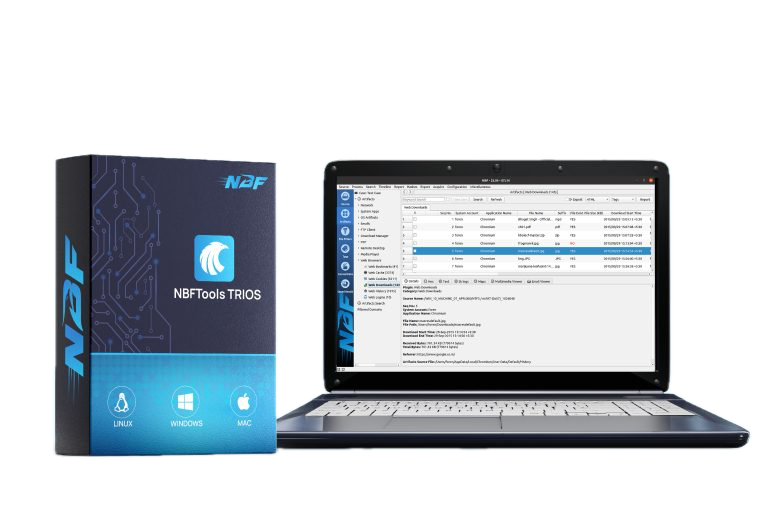
Multi-OS Forensic Analysis
TRIOS is a digital forensics analysis tool that runs on Apple Mac, Microsoft Windows and Linux. It analyses forensic images from Windows, Linux, macOS, servers and USB drives, plus iOS, Android and cloud backups and logically acquired data. Its core engine delivers results quickly on modest hardware.
Monthly Mac license available. Request a license
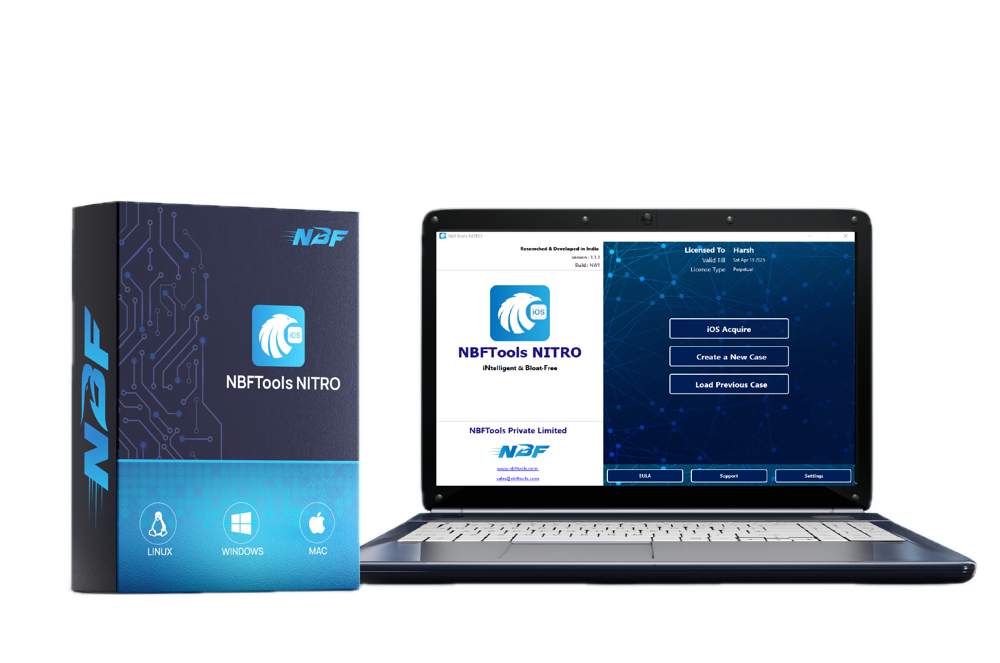
iOS Acquisition & Analysis
NITRO is an iOS acquisition and analysis tool for fast, efficient mobile forensics. It handles triage, acquisition and in-depth analysis in one workflow, keeping hardware requirements low while delivering fast, accurate results.
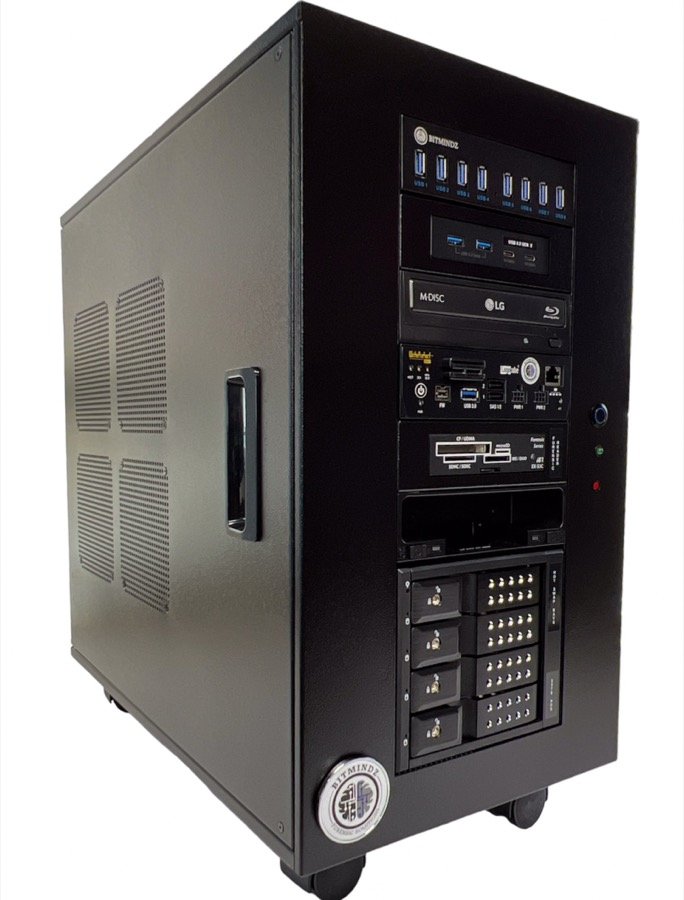
 Built by BitMindz
Forensic Workstations
A top-rated forensic workstation for rapid triage and processing of computer data and forensic images. It pairs a 13th-generation Intel Core i9 with fast PCIe 4.0 NVMe storage and 128GB of DDR5 RAM. Built by NBFTools partner BitMindz, whose team has decades of hands-on forensic experience.
Need something different? Custom configurations are available on request.
Flexible Licensing
Get a license whenever you need one, for as long as you need it. Message us on WhatsApp for current pricing.
Forensic analysis on Apple Mac, Windows and Linux, covering images from macOS, Windows, Linux, servers and USB drives.
Triage and acquisition with Apple Silicon Mac acquisition, T2 decrypted images and selective acquisition.
Send us a request on WhatsApp (+91 99635 67070) or email info@noahforensicsolutions.com and we will arrange your license.
A monthly license is valid for 30 days from activation.
No. The license is tied to the USB serial number you provide and cannot be transferred to another device.
NBFTools
We image Windows and Linux desktops, laptops and devices such as the Microsoft Surface Pro. Our Mac forensics expertise covers every generation of Apple Mac, including Apple Silicon.
Read More about Forensic ImagingAlong with imaging, we analyse forensic images and other data sets across a wide variety of file systems, operating systems, mobile devices and cloud data.
Read More about Forensic AnalysisBeyond imaging and analysis, we help you design your digital forensic processes, from first-response jobs to lab examinations, and set up your lab.
Read More about Consultation ServicesProfessional Services
Certified examiners supporting law enforcement, legal teams and enterprises from acquisition to expert testimony.
Forensic Imaging
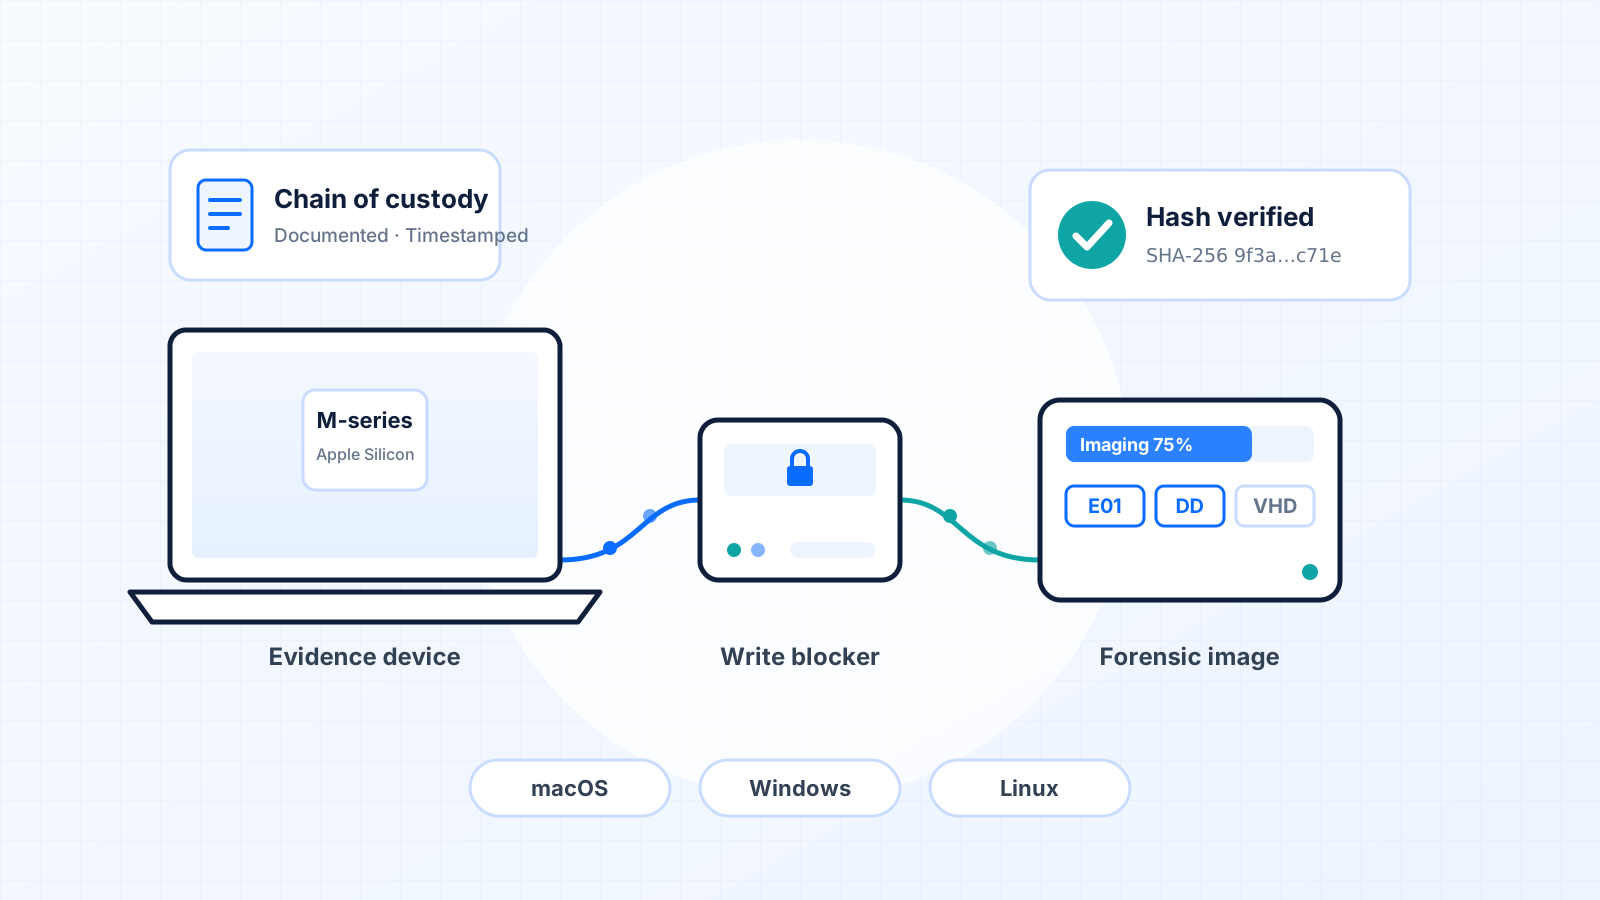
We image Windows and Linux desktops, laptops and devices such as the Microsoft Surface Pro, and every generation of Apple Mac, including the latest Apple Silicon machines. Every image is hashed so it can be verified at any time.
All generations of Apple Mac, including Apple Silicon M-series machines.
Desktops, laptops and specialist devices imaged to forensic standards.
Collect only what matters, by user profile, application or custom filter.
At the scene, in your lab or in ours, with chain of custody maintained throughout.
Forensic Analysis
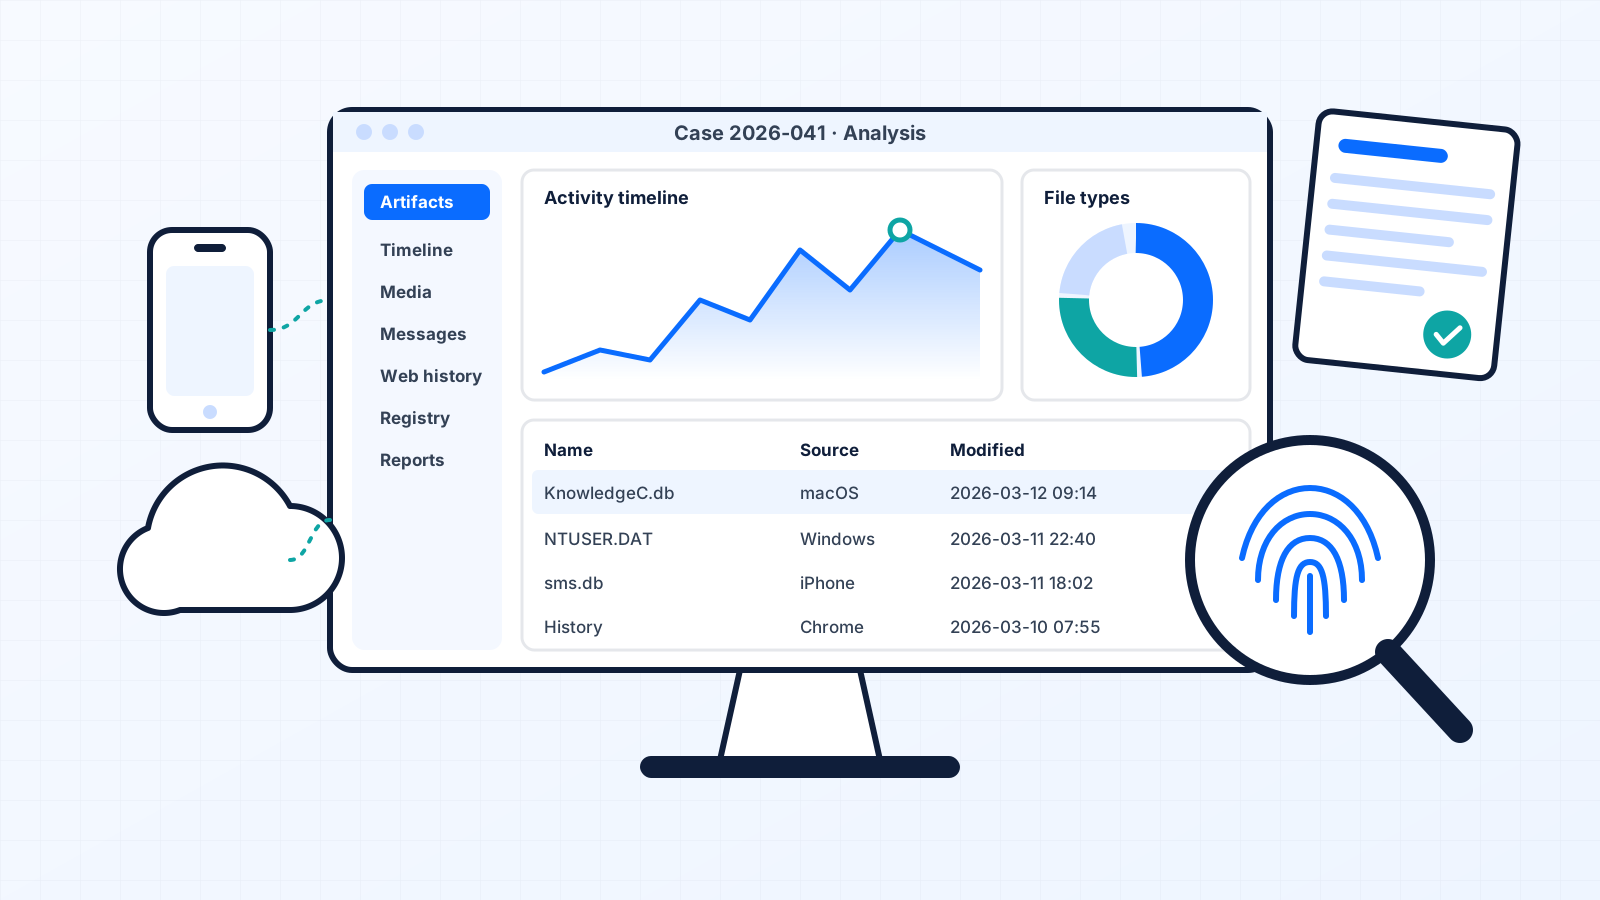
We analyse forensic images and other data sets across file systems, operating systems, mobile devices and the cloud, from Apple Mac, iPhone and iPad to Windows and Linux servers. Our findings come as forensically accurate reports, ready to print, share or present in court.
Apple Mac, iPhone, iPad, Windows, Linux desktop and server file systems.
iOS extractions and evidence held in cloud services.
Clear findings for technical and non-technical readers, with expert testimony when required.
Evidence integrity and chain of custody preserved at every step.
Consultation
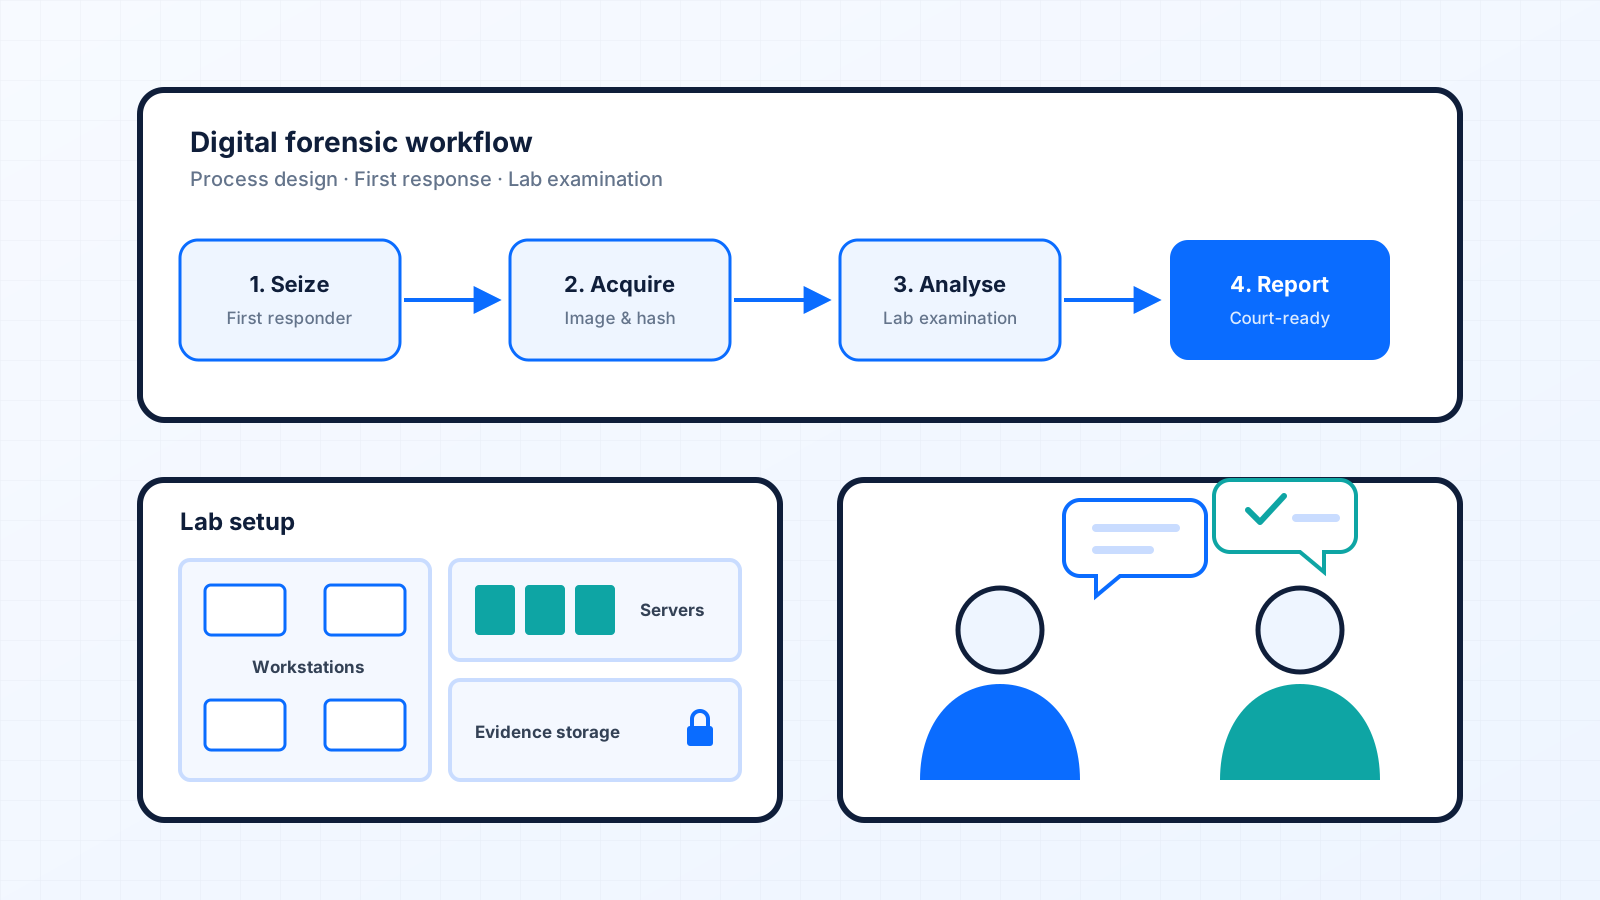
Beyond imaging and analysis, we help you design your digital forensic processes, from first-response jobs to lab examinations. We also draw on our hardware and software expertise to help you set up a complete forensic lab.
Workflows for first responders and lab examiners, built around your organisation.
Layout, equipment, networking, storage and security for a working lab.
Independent guidance on choosing and deploying the right tools.
Ongoing help and training to keep your team current.
Forensic Training
Hands-on courses for examiners at every level, from basic system analysis to advanced data recovery, using industry-standard tools and methods. Take online courses for flexibility or in-person sessions for more interaction. Our instructors have trained professionals across North America, Europe and Asia.
Comprehensive Curriculum
File system analysis, web activity, encryption and deleted data recovery across macOS, Windows and Linux.
Customised to Your Needs
Training shaped around your goals, from first steps to expert level.
Hands-On Training
Practical, real-world exercises that prepare you for live investigations.
Expert Instructors
Seasoned practitioners with 15+ years of casework and a decade of teaching.
Designed for novice and expert examiners alike.
APFS, HFS+, NTFS, ext4, exFAT and FAT.
System configuration, login history and usage timelines.
History, downloads and bookmarks from all major browsers.
macOS security, FileVault and third-party encryption.
Snapshots, data carving and Time Machine backups.
Volatile data acquisition and evidence seizure on macOS and Linux.
In person, on-site or in virtual classrooms.
Programmes that adapt to your needs and experience.
Clear pricing and a simple agreement. Nothing starts until you say go.
We work closely with you so the programme fits, and we are on hand for questions.
Hands-on experience with industry-leading tools and current techniques.
Industry-standard, repeatable procedures aligned with ISO/IEC 27037 guidance.
Cryptographic hashing and full chain-of-custody documentation at every step.
Seasoned examiners with extensive casework and courtroom experience.
Talk with a senior examiner about your case, your devices, and your timeline. Confidential and obligation-free.
WhatsApp or call +91 99635 67070
Book a demo now for free at info@noahforensicsolutions.com
Book Free Demo Now